Crisis Preparedness & Tabletop Exercises
Incident Response Readiness Assessment
Find out what breaks before an incident does. Tyson Martin reviews your response plan, runs the exercise, and gives your board a plan it can act on.
- Know who decides what in the first 48 hours
- Board disclosure rehearsal aligned to SEC Item 1.05 timing
- Updated response plan plus after-action report you can show
Led by Tyson Martin, CISSP, NACD contributor and former security leader at AWS.
Prefer to talk? Call +1 (802) 430-9200
Scope your readiness assessment
Tell us about your organization and where you are today. You'll get a reply from Tyson Martin directly.
What a readiness assessment changes
Decisions, not confusion
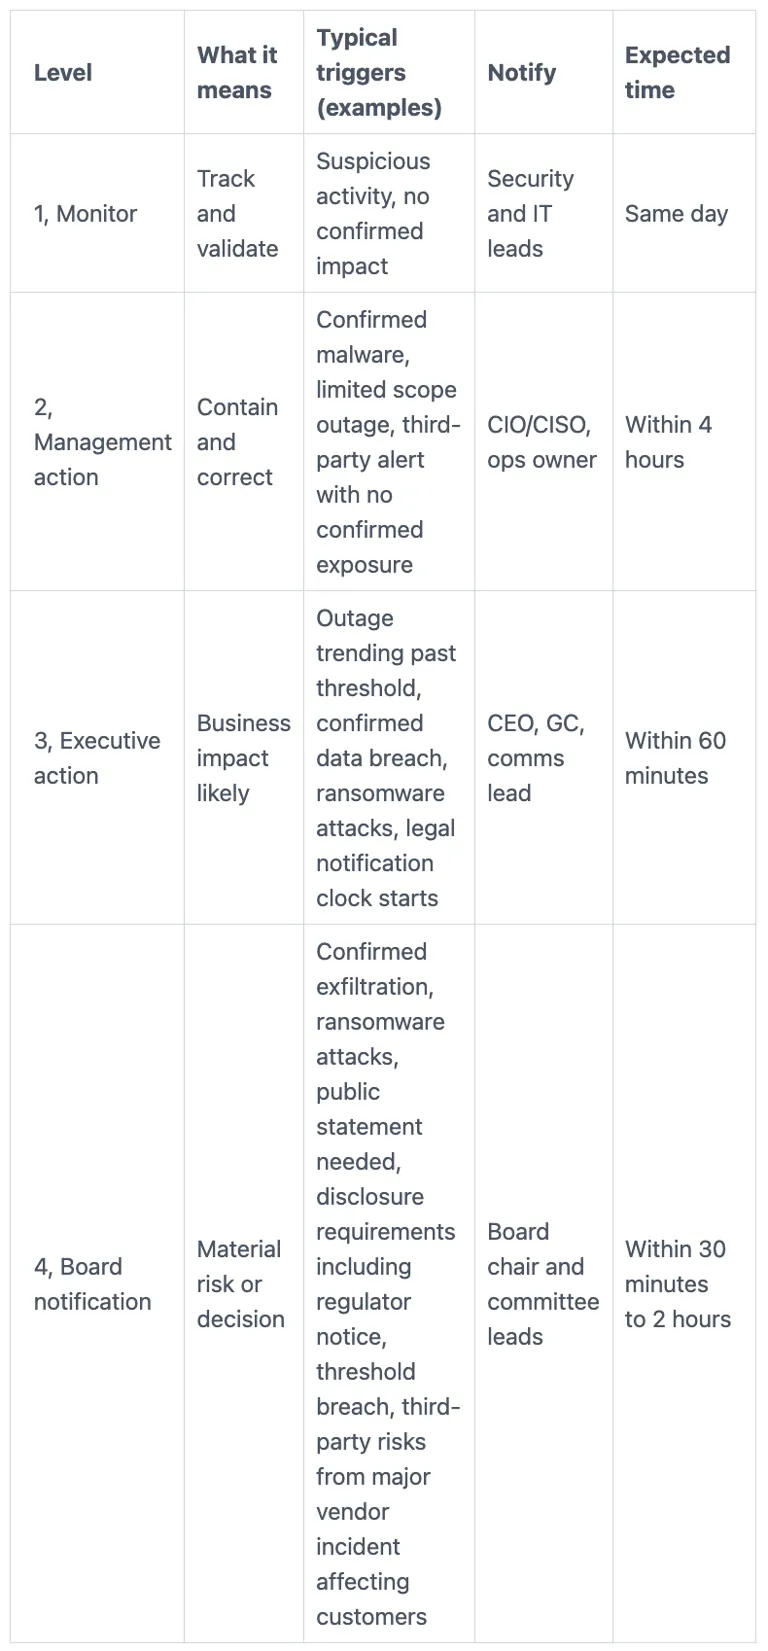
Escalation thresholds and decision rights are written down so they hold up in a real incident.
Board knows its role
Directors get a crisis decision guide so they know what they own and what management owns.
Disclosure practice
A board disclosure rehearsal aligned to SEC Item 1.05 four-day timing, before the clock is live.
Plain-English findings
Technical risk is translated into business impact: downtime, vendor exposure, disclosure duties.
Evidence you can show
An after-action report and updated plan that document the work for auditors and regulators.
Independent view
An outside advisor validates whether the program matches what the board has been told.
What the assessment covers
The assessment prepares boards, executives and response teams for the hours and days after a cyber incident. It is a guided review and exercise, not a penetration test or a technical audit.
Work is scoped to your organization. A tabletop is built around a scenario you could actually face, and the findings feed a plan with owners and dates.
- Incident response readiness review of your current plan and gaps
- Customized tabletop exercise for the board, executives or response team
- Board disclosure rehearsal aligned to SEC Item 1.05 four-day timing
- Backup and restore validation
- Updated incident response plan
- Board-level disclosure playbook
- Tabletop after-action report
- Director crisis decision guide
Who this work comes from
“Tyson Martin brings the full package: deep technical expertise, functional clarity, and the leadership presence to rally teams when it matters most. He's one of the few security leaders I've worked with who truly understands how to design, deploy, and operationalize SIEM solutions that generate real business insight, not just noise. When incidents arise, Tyson leads with calm urgency, aligning stakeholders, containing threats, and preserving trust. His ability to connect the dots between architecture, governance, and response makes him a standout in the field.”
“Tyson Martin has a unique ability to translate complex cybersecurity risks into actionable business insights which helped our executive team make informed strategic decisions.”
“What sets Tyson apart is his ability to translate cybersecurity into strategic growth language for boards. He builds frameworks that don't just mitigate risk, they enable competitive advantage. He's exactly who you want guiding your organization in high-trust environments.”
What happens after you ask
Short scope call
We talk through your plan, your board's expectations and what you want the exercise to test.
Written proposal
You get a clear scope, deliverables and fee for the readiness review and tabletop.
Run and report
We run the review and exercise, then hand over the after-action report and updated plan.
Frequently asked questions
Is this a penetration test or a technical audit?
No. This is a governance and readiness engagement. Penetration testing and technical security audits are outside the practice's scope.
Who should take part?
The exercise can be built for the board, the executive team, the response team, or a mix. Directors receive a crisis decision guide so they know their role.
What does it cost?
Pricing depends on scope: who takes part, how many sessions, and whether it is virtual or on site. You get a written scope and fee after a short call.
Can you run it remotely?
Yes. Engagements are delivered nationwide across the US, remote or on site.
Does this cover SEC disclosure obligations?
The engagement includes a board disclosure rehearsal aligned to SEC Item 1.05 four-day timing and a board-level disclosure playbook. It is advisory work, not legal advice.
What do we get at the end?
An updated incident response plan, a board-level disclosure playbook, a tabletop after-action report and a director crisis decision guide.
Test your response before an attacker does
Tell us who needs to be ready and what worries your board. You'll get a scope, deliverables and a fee in writing.
- Know who decides what in the first 48 hours
- Board disclosure rehearsal aligned to SEC Item 1.05 timing
- Updated response plan plus after-action report you can show
Prefer to talk? Call +1 (802) 430-9200