Board-Level Cyber & AI Risk Advisory
Cybersecurity Advisory Services for Boards and Executives
Independent advice from a CISSP-certified advisor who has led security at AWS, Home Depot and Best Buy. Clear oversight, credible reporting, defensible decisions.
- Plain-English risk reporting your board can act on
- Decision rights and escalation that hold in a real incident
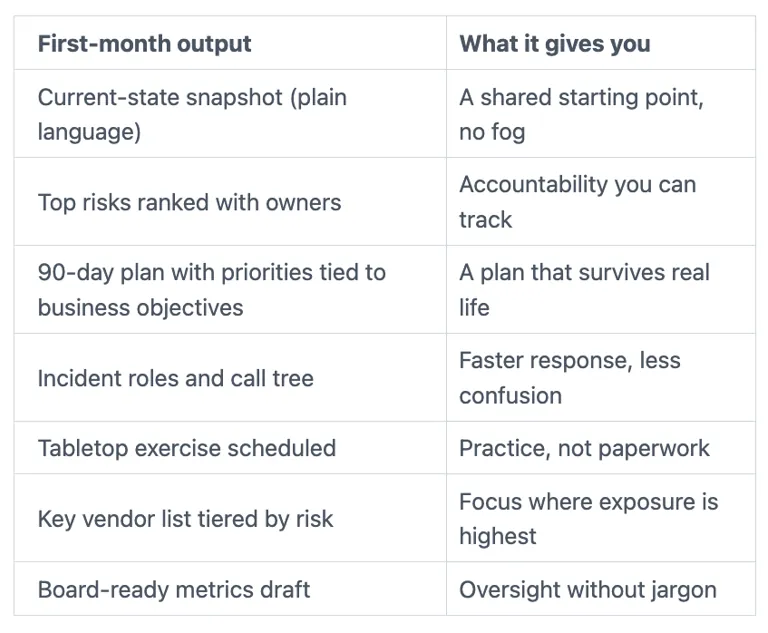
- A 90-day plan with named owners and measurable outcomes
CISSP. NACD member. NRF CISO Executive Committee. World Economic Forum contributor.
Prefer to talk? Call +1 (802) 430-9200
Talk about your cyber risk oversight
Tell us what your board or executive team needs. You will get a scoped proposal back.
Why boards choose this advisory practice
Technical risk in plain English
You get your risk posture and what changed since the last briefing in language directors understand.
Independent of your vendors
No tools, software or managed services are sold here. The advice is not tied to any product.
Decisions, not data dumps
One-page reporting and a stable dashboard that shows trend, not trivia, so the board can decide.
Enterprise-tested judgment
Security and technology leadership experience at AWS, Home Depot and Best Buy, applied to your board.
Evidence of duty of care
Risk appetite statements, decision-rights matrices and review cadence you can show regulators.
Senior leadership when you need it
Interim CISO stabilization or ongoing fractional CISO, CIO and Chief Digital Officer leadership.
What cybersecurity advisory services cover
This is an advisory practice, not a product company. Engagements range from a half-day board workshop to a long-term advisory retainer, an interim CISO stabilization, or a fixed-scope due diligence review. Every engagement ends with something you can inspect: a written plan, a scorecard, a dashboard or a one-page board briefing.
Work is delivered across the United States, remote or on site, with stated focus areas in Maine, Richmond VA and the Chicago area.
- Board Risk Advisor retainer: quarterly plain-English reporting and between-meeting access
- Board Cyber & AI Clarity Intensive: half-day or full-day workshop with a 90-day action plan
- Cybersecurity Program Assessment: maturity scorecard and prioritized remediation roadmap
- Technology and cyber risk appetite statement with a board decision-rights matrix
- AI risk governance: AI risk register, board AI policy and employee AI use policy
- Interim CISO for 30 to 90 days, or ongoing fractional and virtual CISO leadership
- M&A cyber due diligence: target risk profile, red-flag memo and valuation impact
- Crisis tabletop exercises and SEC Item 1.05 disclosure rehearsal
- Third-party and vendor risk reporting built for the board
Experience behind the advice
“What sets Tyson apart is his ability to translate cybersecurity into strategic growth language for boards. He builds frameworks that don't just mitigate risk, they enable competitive advantage. He's exactly who you want guiding your organization in high-trust environments.”
“Tyson Martin embodies what modern boardrooms need: a leader who brings clarity, credibility, and strategic foresight to every technology conversation. Tyson is what every Board is seeking in 2025, someone who understands technology and can interpret and speak to Boards with a message Boards can understand. In doing so, Tyson doesn't just support governance, he elevates it.”
“Tyson Martin has a unique ability to translate complex cybersecurity risks into actionable business insights which helped our executive team make informed strategic decisions.”
What happens after you reach out
Share your situation
Send the form. You describe the board, committee or executive need and what triggered it.
Scoping conversation
A direct call with Tyson Martin to confirm the question you need answered and who needs to hear it.
Written scope and proposal
You get a defined engagement with deliverables, cadence and outcomes before any work begins.
Frequently asked questions
How is pricing set?
Pricing depends on the engagement type and scope. Some offerings, such as the AI Governance Starter Pack, are fixed-fee sprints. Others are retainers, workshops or defined assessments. Send your details and you will get a scoped proposal.
Do you sell security tools or monitoring?
No. This practice does not sell products, resell vendors, run a SOC or provide 24x7 monitoring. That independence is the point: the advice is not tied to anything being sold.
Do you do penetration testing or technical audits?
No. Penetration testing and technical security audits are out of scope, as is building or tuning AI models. The work is governance, oversight, assessment and executive leadership.
Can you work with our existing CISO?
Yes. Advisory support for an in-house CISO includes board-communication coaching, an independent sounding board on priorities, audit and board cycle prep, and independent validation that the program matches what the board is told.
Where do you work?
Across the United States, remote or in person. Stated focus areas include Maine (Bangor and Augusta), Richmond VA and the Chicago area. Non-US markets are not served.
Can you guarantee we will not be breached?
No. No advisor can promise zero risk or breach-proof security. What you get is clearer decision rights, faster escalation, stable metrics and a plan you can evidence.
Get an independent view of your cyber risk
Tell us about your board, committee or executive team and the decision in front of you. You will get a clear scope back, with deliverables and outcomes defined before work starts.
- Plain-English risk reporting your board can act on
- Decision rights and escalation that hold in a real incident
- A 90-day plan with named owners and measurable outcomes
Prefer to talk? Call +1 (802) 430-9200